Audit, compliance, and governance are often treated as something that comes after the system is built.
Once the product works, once the data is consistent, once the flows are automated, we add controls. We introduce checks, approvals, reports, and sign-offs. We build layers on top of the system to make it auditable, compliant, and governable.
And yet, in many organisations, audits are still painful. Compliance reviews still trigger frantic reconstructions of what happened. Governance processes still rely on manual explanations, spreadsheets, and tribal knowledge.
The problem is not a lack of controls. The problem is that the system does not remember the story the business already knows.
In the previous posts, I argued that “current state” is a dangerous lie in decision-heavy systems. It hides time, sequence, and context behind a single snapshot that looks authoritative but explains very little. That same lie sits at the heart of many audit and compliance problems.
Auditors do not ask, “What does the system look like now?” They ask, “How did we get here?”
They want to understand which facts were known at the time, which rules applied, which decisions were made, and why those decisions were valid given what was known then. In other words, they are not asking for state. They are asking for history with meaning.
This is why so many audit processes feel like archaeology.
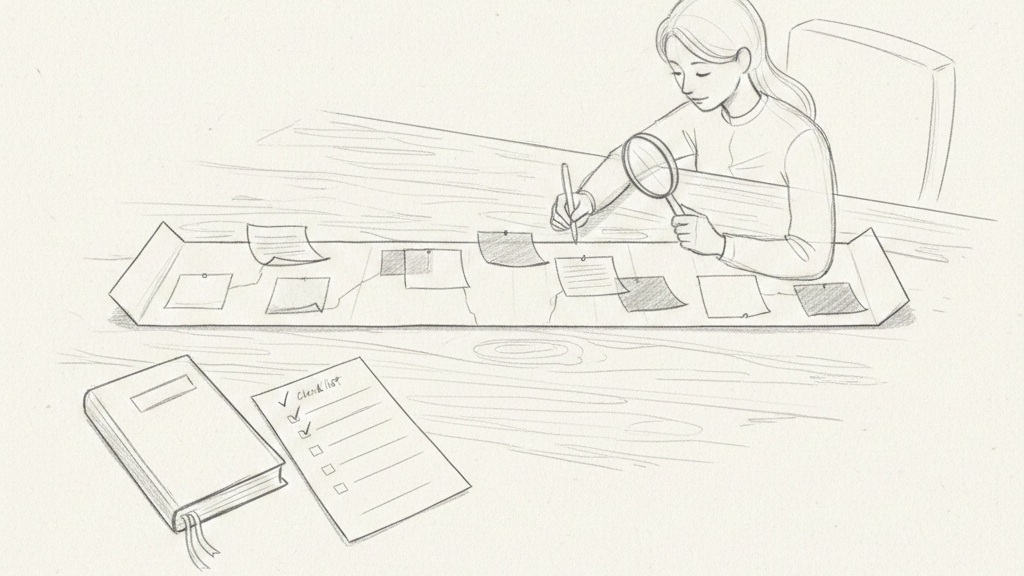
Teams dig through logs, reconstruct timelines, compare versions, and try to infer intent after the fact. Screenshots are taken. Queries are written. People are interviewed. Explanations are stitched together manually, often weeks or months after the decision was made.
None of this happens because auditors enjoy complexity. It happens because the system flattened reality into “now” and discarded the narrative along the way.
From a business perspective, the story is usually clear.
A policy was active. A premium was missed. The policy lapsed. A reinstatement was approved, effective from a certain date. A claim occurred. A pay-out decision was made based on what was valid at that moment.
This story exists in people’s heads. It exists in procedures, training materials, and legal reasoning. What often does not exist is a system representation that preserves this story from start to finish.
This is where an event-centric perspective changes everything — not by adding governance features, but by refusing to erase business memory.
When a system is built around facts over time, auditability is no longer something you bolt on. It is a natural property of the model.
Each event answers a simple question: what happened? Each decision answers another: why was this allowed at that time?
There is no need to reconstruct the past, because the past was never overwritten.
Compliance, too, becomes less about policing and more about traceability.
Rules are not enforced by retroactive checks on current state, but by evaluating decisions in the context in which they were made. If a regulation changed last year, the system does not pretend it always applied. It knows when it came into force and which decisions were subject to it.
This distinction matters enormously in regulated domains. It separates non-compliance from historical correctness. It allows organisations to say, with confidence: this decision complied with the rules that applied at the time.
That is a very different statement from “the system currently looks compliant”.
Governance follows the same pattern.
Good governance is not about freezing systems or slowing teams down. It is about being able to explain decisions, delegate responsibility, and reason about risk. None of that requires more approval steps. It requires clarity about who decided what, when, and based on which facts.
When systems preserve that clarity, governance becomes quieter. Less performative. Less reactive. The conversations shift from “prove that this is okay” to “here is why this was okay”.
What’s striking is that none of this requires additional effort from the business.
The business already thinks this way. It already reasons in timelines, decisions, and context. Audit, compliance, and governance are already grounded in stories, not snapshots.
The friction appears when systems insist on collapsing those stories into state.
Seen this way, #EventModeling is not an audit technique. It is not a compliance framework. It is not a governance process.
It is simply a commitment to preserve business reality as it unfolds — to model what happened instead of constantly rewriting it into something that looks tidy in the present.
Once that commitment is made, many of the controls we add later become less critical. Not because governance disappears, but because the system finally speaks the same language as the people responsible for it.
Audit, compliance, and governance do not need more machinery.
They need the story the business already knows — and systems that are willing to remember it.
Prior posts in the series:
- Post 1: We lack a shared language and blueprint
- Post 2: We can work with a small set of repeatable building blocks
- Post 3: We need a living map for the enterprise
- Post 4: When “change state” quietly reshapens our boundaries
- Post 5: Where does a domain get the facts it needs to make a decision?
- Post 6: Boundaries Follow Decisions, Not Data
- Post 7: When software makes simple business decisions hard
- Post 8: Why Systems Forget What the Business Never Did
- Post 9: Why EventModeling Still Struggles in the Enterprise
- Post 10: Why “Current State” Is a Dangerous Lie in Decision-Heavy Systems
Originally published on LinkedIn (2026-01-12): https://www.linkedin.com/pulse/audit-compliance-governance-dont-need-more-controls-story-schenker-pw04e